# Setup
Support for other authentication providers coming soon! Please contact us to request support for your organization's authentication provider.
{% content-ref url="/pages/n7BtlSv9JlpJ0wVMQOSI" %}
[Okta](/setup/okta)
{% endcontent-ref %}
# Okta
{% content-ref url="/pages/qZyCHYPQdqfzEZ7hAz6b" %}
[Access Your Domain](/setup/okta/access-your-domain)
{% endcontent-ref %}
{% content-ref url="/pages/8vy84uaCY7BjIukK4UhX" %}
[Create an App Integration; Access Your Client ID and Client Secret](/setup/okta/create-an-app-integration-access-your-client-id-and-client-secret)
{% endcontent-ref %}
{% content-ref url="/pages/I5UJpORacA60Xaov5CYb" %}
[Add a User](/setup/okta/add-a-user)
{% endcontent-ref %}
# Access Your Domain
* [ ] Log in to Okta
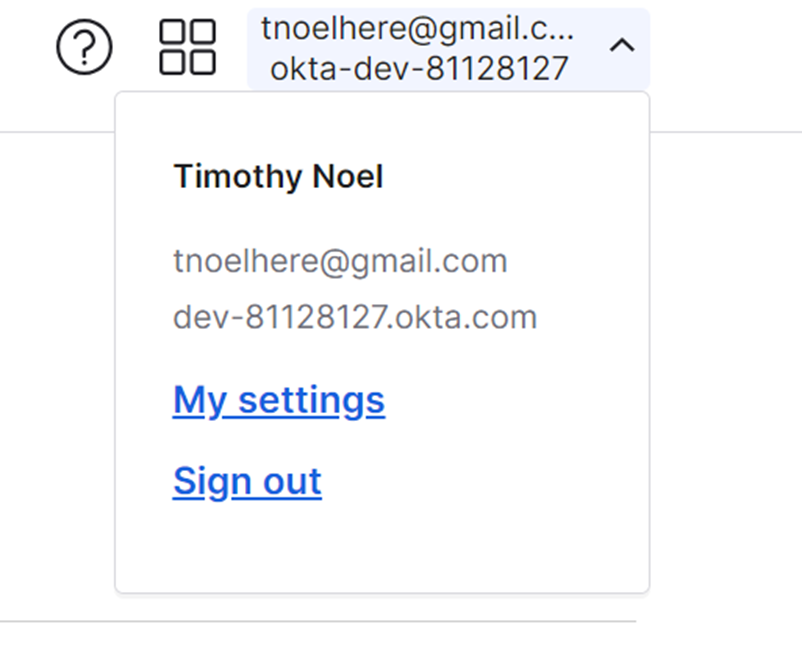
* [ ] Click the account dropdown menu located in the top-right corner of your window
* [ ] Your organization's Okta domain will appear in the dropdown menu
# Create an App Integration; Access Your Client ID and Client Secret
* [ ] Log in to Okta
* [ ] Navigate to the Applications page by clicking the "Applications" dropdown menu in the navigation bar on the left side of your window and then clicking the "Applications" dropdown item
* [ ] Create a new app integration by clicking the "Create App Integration" button
* [ ] Choose "OIDC - OpenID Connect" as the sign-in method and "Web Application" as the application type for your app integration and click the "Next" button to proceed to the next page
* [ ] Select the "Client Credentials" and "Authorization Code" grant types and enter ** as the sign-in redirect URI
* [ ] Configure the other settings for your app integration and click the "Save" button to create your app integration
* [ ] The Client ID for the app integration you created for EVA will appear in the "Client Credentials" section of the "General" tab of the details view for the application
* [ ] The Client Secret for the app integration you created for EVA will appear in the "Client Credentials" section of the "General" tab of the details view for the application
* [ ] Ensure that the Okta Authorization Server you plan to use with EVA is equipped with an Access Policy and associated Policy Rule(s) that permit your organization's users to authenticate themselves when redirected to Okta from EVA. To learn more about Access Policies and how to create one, if needed, [read Okta's docs](https://developer.okta.com/docs/guides/configure-access-policy/main/).
# Add a User
* [ ] Log in to Okta
* [ ] Navigate to the People page by clicking the "Directory" dropdown menu in the navigation bar on the left side of your window and then clicking the "People" dropdown item
* [ ] Add a new user by clicking the "Add Person" button
* [ ] Enter the information for the new user and click the "Save" button to add them
# Determine How Often to Prompt Users for Re-Authentication or Multi-Factor Authentication
By default, Okta will utilize session cookies to automatically authenticate users when they are redirected to Okta from EVA. If your organization's use case for EVA necessitates overriding this out-of-the-box behavior, follow these steps to instruct Okta how often users are required to re-authenticate or complete multi-factor authentication when signing in:
* [ ] Log in to Okta
* [ ] Navigate to the Applications page by clicking the "Applications" dropdown menu in the navigation bar on the left side of your window and then clicking the "Applications" dropdown item
* [ ] Select the app integration you created for EVA
* [ ] Navigate to the "Sign On Policy" section of the "Sign On" tab of the details view for the application
* [ ] Add a new application sign-on rule by clicking the "Add Rule" button
* [ ] If you want to determine how often Okta prompts users to re-authenticate themselves when redirected from EVA, select the "Prompt for re-authentication" option and enter a timeout duration appropriate for your use case
* [ ] If you want to determine how often Okta prompts users to complete multi-factor authentication when redirected from EVA, select the "Prompt for factor" option and choose an interval appropriate for your use case
* [ ] Configure the other settings for your application sign-on rule and click the "Save" button to create your rule
# Contact Us
Reach out to us at if you have any issues with our products.